Repository navigation
feat(ui): policy-aware provider picker + dev nav - #3339
Merged
smakosh merged 3 commits intoJul 31, 2026
Merged
Conversation


The compliance page's provider dropdowns now show whether each
provider meets the policy's certification, data-policy, and
headquarters requirements (green/red shield + the exact failing
requirements), with a toggle to hide incompatible providers.
Indicators deliberately ignore the allow/block lists themselves so
an active allow list doesn't paint every candidate red.

The Provider Impact counter now includes custom providers, and the
allowed-empty state no longer claims all requests will be blocked
when a compliant custom provider exists.

Project-scoped developers get an Organization > Custom Models
sidebar entry pointing at the read-only catalog view.

Claude-Session: https://claude.ai/code/session_01Vd3toRu4u6fU9quL7XjbC3

Contributor
|
Important Review skippedAuto reviews are disabled on base/target branches other than the default branch. Please check the settings in the CodeRabbit UI or the ⚙️ Run configurationConfiguration used: Repository UI Review profile: CHILL Plan: Pro Plus Run ID: You can disable this status message by setting the Use the checkbox below for a quick retry:
Thanks for using CodeRabbit! It's free for OSS, and your support helps us grow. If you like it, consider giving us a shout-out. Comment |
Native span[title] tooltip on the selected-chip warn shield instead
of an svg <title> child, a policy-specific empty state when the
compatible-only filter hides everything, and narrowed types instead
of non-null assertions.

Claude-Session: https://claude.ai/code/session_01Vd3toRu4u6fU9quL7XjbC3

smakosh
merged commit Jul 31, 2026
047d7e5
into
developer-models-compliance-visibility
8 checks passed
pull Bot
pushed a commit
to soitun/llmgateway
that referenced
this pull request
Aug 5, 2026

## Problem

The July traffic report showed revenue concentrating in two places we
under-serve:

1. **The DevPass dashboard is the #1 converting surface** (354 payers
last month), and Reset Passes sold 42 units in month one with zero
targeting — but the agreed follow-up from theopenco#3093 (a real cap-hit
analytics event) never shipped, and the dashboard shows the same
ResetPassCard at 0% and 100% usage. No contextual offer exists at the
moment of highest intent.
2. **Compliance content converts payers at ~5%** (soc2-type-ii: 158
readers → 8 payers) but enterprise leads are flat at 4/month — the post
never presents the enterprise path. Meanwhile the weekly report shows
organic momentum fading, with the proven "[X] alternatives" and Kimi K3
playbooks sitting unshipped.

## What this ships

### DevPass: cap-hit funnel + contextual offer

- **`devpass_premium_cap_rejected`** captured server-side in the gateway
when the weekly premium-cap 402 fires
(`assertDevPlanPremiumCapNotExceeded`), with `devPlan`, `model`,
`msUntilReset`, and org group. This is the follow-up agreed in theopenco#3093:
`devpass_weekly_cap_hit_viewed` only counts users who open the
dashboard, but most cap hits happen inside coding agents that swallow
the 402 — demand was undercounted. Adds a `posthog-node` client to
`apps/gateway` (mirrors `apps/api/src/posthog.ts`; disabled without env,
no hot-path cost).
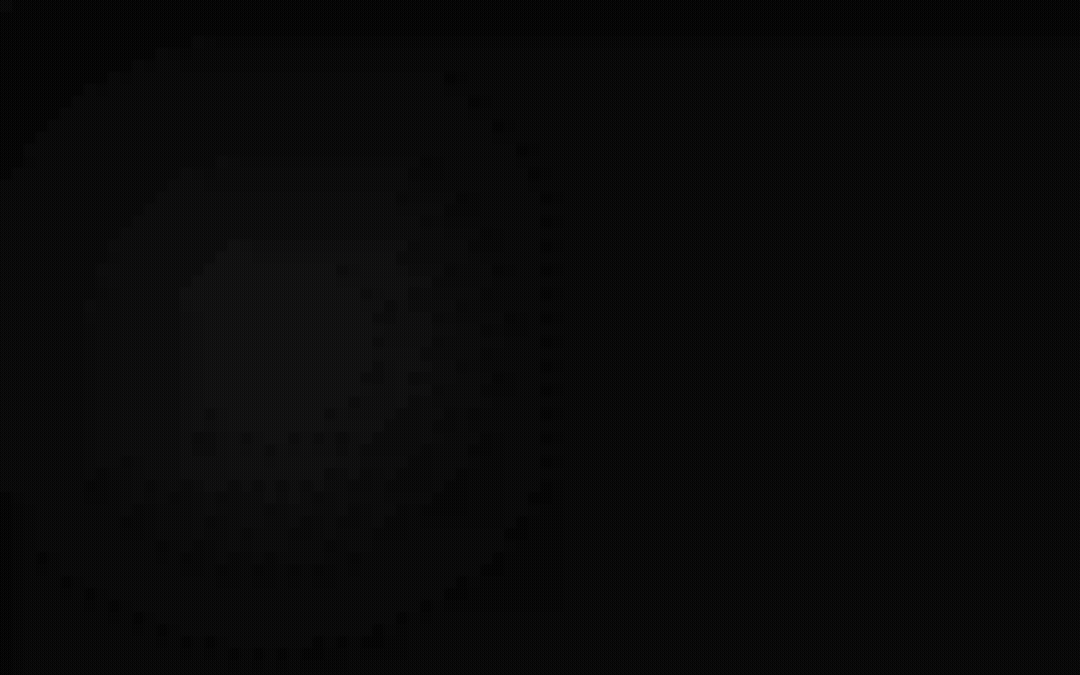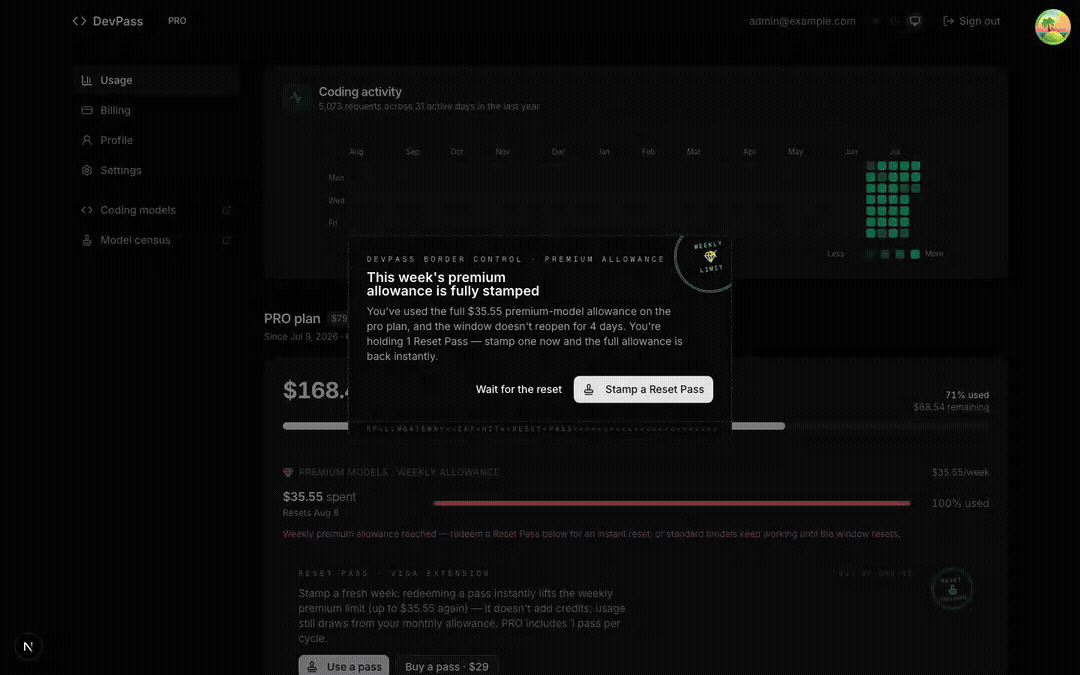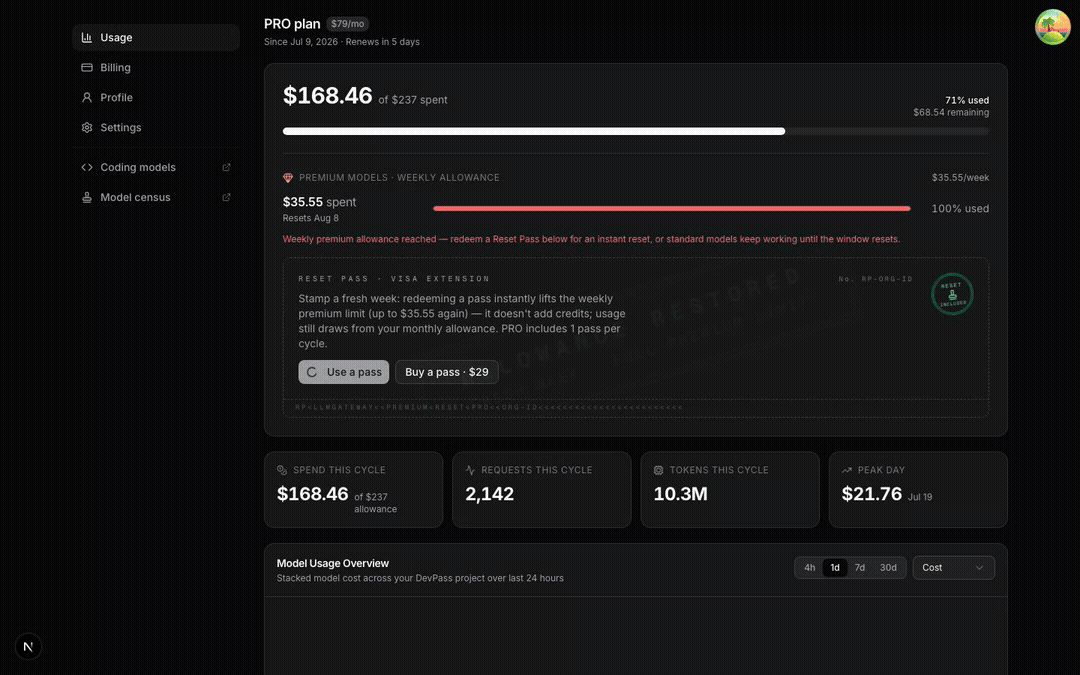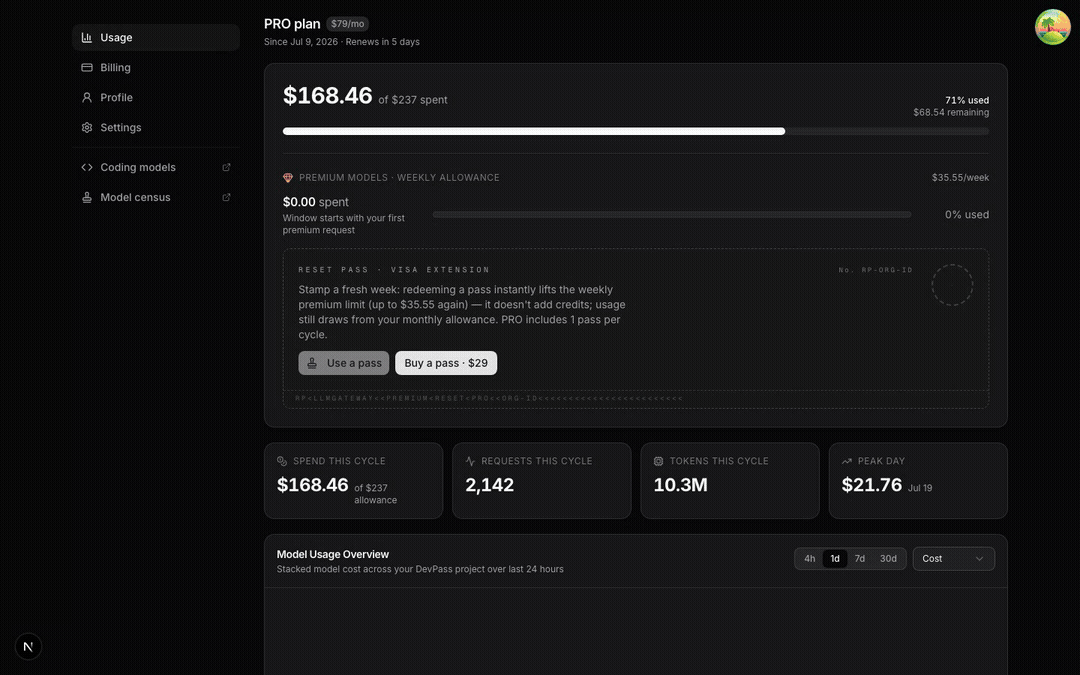
- **`CapHitResetOfferDialog`** on the DevPass dashboard: a visa-stamp
dialog (border-control stamp, MRZ strip — house DevPass brand) that
appears the moment the weekly premium cap is hit, driven by the existing
5s status poll. It mirrors the server's purchase/redeem gates (never
offers an action the API would 400), stays quiet when the monthly pool
is exhausted (that state belongs to `AllowanceExhaustedCard`), snoozes
per cap-window via cookie, and emits
`devpass_cap_hit_offer_shown/dismissed/clicked`. The CTA scrolls to the
ResetPassCard rather than duplicating the purchase surface.
- **`/ingest` PostHog proxy for `apps/code`** (mirroring apps/ui and
apps/playground) — DevPass dashboard events were ad-blocker-droppable
until now, so July's 500 cap-hit views were an undercount. Expect an
event step-up after deploy.

<img width="1080" alt="Cap-hit Reset Pass offer demo: dialog appears at
100% weekly usage, CTA scrolls to the ResetPassCard, redeem restores the
allowance"
src="https://raw.githubusercontent.com/theopenco/llmgateway/cc22b375431e6148e4889e403c4635327095fc0c/cap-hit-reset-pass-demo.gif"
/>

([MP4
version](https://raw.githubusercontent.com/theopenco/llmgateway/cc22b375431e6148e4889e403c4635327095fc0c/cap-hit-reset-pass-demo.mp4))

### Compliance/enterprise content cluster

- `soc2-type-ii` gains a **provider compliance policies** section (the
theopenco#3339 policy-aware picker, fail-closed requirements, 403-before-egress),
a proper enterprise CTA block, and links into the new cluster.
- Three sibling posts feeding the same funnel: **`llm-data-retention`**,
**`gdpr-compliant-llm-routing`**, and **`llm-compliance-checklist`** —
all fact-checked against
`apps/docs/content/features/{data-retention,compliance}.mdx` and the
routing docs (region example uses a real catalogue mapping,
`aws-bedrock/claude-sonnet-4-6:eu-west-2`).
- New **`BlogCta variant="enterprise"`** (→ `/enterprise#contact` +
`/enterprise/compliance`) used by all three.

### Organic pipeline refill

- **`portkey-alternatives`** and **`helicone-alternatives`** listicles —
the two SERP gaps left open after the litellm/openrouter/copilot
listicles proved the pattern. Facts per the verified June-2026
competitor landscape (Portkey→Palo Alto/Prisma AIRS; Helicone→Mintlify
maintenance mode; Langfuse/LangSmith claims re-verified this week).
Internal links added from `/compare/portkey`, the vs-Portkey post,
best-ai-gateways, and both existing listicles' "skip" sections.
- **Kimi K3 spokes**: `kimi-k3-open-weights` (weights shipped Jul 26 on
HF under a custom **"Kimi K3 License"** — not the Modified MIT press
predicted, so the post and pillar deliberately point at the LICENSE file
instead of summarizing terms) and `kimi-k3-api` (the "kimi k3 api"
query; reasoning_effort semantics, cached-input economics, sticky
sessions). Pillar updated: weights-release facts corrected, spokes
interlinked.
- **`/rankings` interlinks** from the `/models` SEO copy and `llms.txt`
(it had no entry there).
- 7 OG images generated in the house circuit-board style with the
composited wordmark.

## Verification

- `pnpm format`, full `pnpm build`, and `dev-plans-reset-passes.spec.ts`
(32/32) pass.
- Demo recorded against the local stack with the real seed org: staged
cap-hit via SQL (millisecond-truncated `dev_plan_premium_week_start` for
the CAS), dialog fired, CTA scrolled to the card, redeem zeroed
`devPlanPremiumCreditsUsed` and consumed the included pass server-side.

## Notes for review / follow-ups

- The census dialog and the new cap-hit dialog can theoretically stack
(both Radix dialogs; census mounts globally, cap-hit on the main
dashboard page). In the wild both firing together should be rare; if we
care, a simple priority gate in `DashboardShell` would fix it.
- The premium-cap 402 still has no machine-readable `code`
distinguishing it from out-of-credits — agents can't react
programmatically. Left out deliberately (error-shape compatibility);
worth its own PR.
- Blog listicles ship FAQ sections but blog posts emit no FAQPage
JSON-LD (model pages do). Separate SEO follow-up.
- dev.to syndication for the new listicles is intentionally not part of
this PR (staggering per the syndication policy).

🤖 Generated with [Claude Code](https://claude.com/claude-code)

https://claude.ai/code/session_018NeUff4XEsqAVuJRZ8KuvS

<!-- This is an auto-generated comment: release notes by coderabbit.ai
-->
## Summary by CodeRabbit

- **New Features**
- Added a dashboard offer for eligible users who exhaust weekly premium
usage, including reset-pass redemption and purchase options.
- Added links to live model rankings and expanded enterprise compliance
calls to action.
- Added guidance for Kimi K3, GDPR-compliant routing, LLM compliance,
data retention, and gateway alternatives.

- **Documentation**
- Updated model, compliance, licensing, and comparison content with new
articles, refreshed links, and recommendations.

- **Bug Fixes**
- Improved analytics loading, routing reliability, and shutdown
handling.
<!-- end of auto-generated comment: release notes by coderabbit.ai -->

---------

Co-authored-by: Luca Steeb <contact@luca-steeb.com>
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment
1 participant

Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Summary
Stacked on #3335 (base branch is
developer-models-compliance-visibility; GitHub will retarget tomainwhen that PR merges — only the last two commits are new here).Completes the remaining asks from the enterprise customer report that #3335 addressed:
1. "How can I tell which providers meet my compliance requirements when adding an allowed provider?"
The provider dropdowns on the compliance page are now policy-aware:
2. "What do the different colors represent?"
The unexplained dot in the picker was the provider's brand color and carried no compliance meaning. In the compliance context it is replaced by the meaningful shield indicators with an in-dropdown legend, and the docs now spell out what every indicator/color means (impact chips, shields, brand dots elsewhere).
3. Developer-role discoverability (follow-up to #3335's read access)
#3335 made the custom-models catalog readable for developers, but their sidebar had no path to it. Developers now get an Organization → Custom Models entry pointing at the read-only catalog, and the docs recommend this as the way for developers to see available providers/models without extra permissions.
Also fixes the Provider Impact counter to include custom providers ("0 of 45 providers meet this policy… Requests will be blocked" previously showed even when the org's allow-listed custom provider was fully compliant; it now reads "0 of 45 catalogue providers meet this policy. 1 of 2 custom providers comply." and the empty state says only compliant custom providers can serve requests).
The
MultiProviderSelectorchanges are backward-compatible: options withoutmeetsPolicyrender exactly as before (brand-color dot, no toggle/legend), so the API-keys and IAM usages are unaffected.Testing
pnpm test:unit— 208 files, 3457 tests pass.pnpm build— all 17 tasks pass.pnpm formatclean.https://claude.ai/code/session_01Vd3toRu4u6fU9quL7XjbC3