Release: auto-switch profiles for cross-profile session links (#5419) - #5728
Merged
Merged
Conversation


A valid session:// deep link to a session owned by a DIFFERENT Hermes
profile used to look identical to a deleted session (404 -> frontend
self-heals away). Now GET /api/session returns a structured 409
session_profile_mismatch envelope (error/code/session_id/profile ONLY,
no transcript) ONLY when the owning profile is KNOWN, and loadSession()
catches it, switches to the owning profile, and retries once. Truly
missing/deleted or legacy None-profile sessions keep the 404 self-heal.

Gate fixes applied (Codex + Fable):
- Codex CORE: added a post-await stale-load guard after
  _switchProfileForSessionLoad so a navigation during the switch can't
  hijack the UI back to the old session.
- Fable Finding 1: only emit 409 when _session_profile is truthy;
  a None-profile (missing/legacy) session under a non-default active
  profile now keeps 404 instead of a useless profile=null 409 (which
  skipped self-heal + spun the SSE reconnect against a dead sid). Both
  detail branches. + 2 regression tests.
- Fable Finding 2: _switchProfileForSessionLoad now clears the sidebar
  skeleton + re-renders from cache on switch-POST failure (mirrors the
  #4671 canonical-switch catch), then rethrows, so a failed switch can't
  strand the sidebar on the skeleton.

Reconciled tests/test_issue1611_session_profile_filtering.py (4 tests) to
the 409 contract while preserving the no-leak boundary assertion.

Co-authored-by: nesquena-hermes <nesquena-hermes@users.noreply.github.com>

Contributor

| @@ -12061,6 +12080,20 @@ def handle_get(handler, parsed) -> bool: | |||
| cli_meta = _lookup_cli_session_metadata(sid) | |||

Contributor
There was a problem hiding this comment.

When a session:// link points to a CLI session owned by another profile, this lookup still uses the active-profile-only default, so it returns no metadata and _session_profile becomes None. That sends the request down the 404 self-heal path instead of the new session_profile_mismatch response, so valid cross-profile CLI links are still treated as deleted sessions.


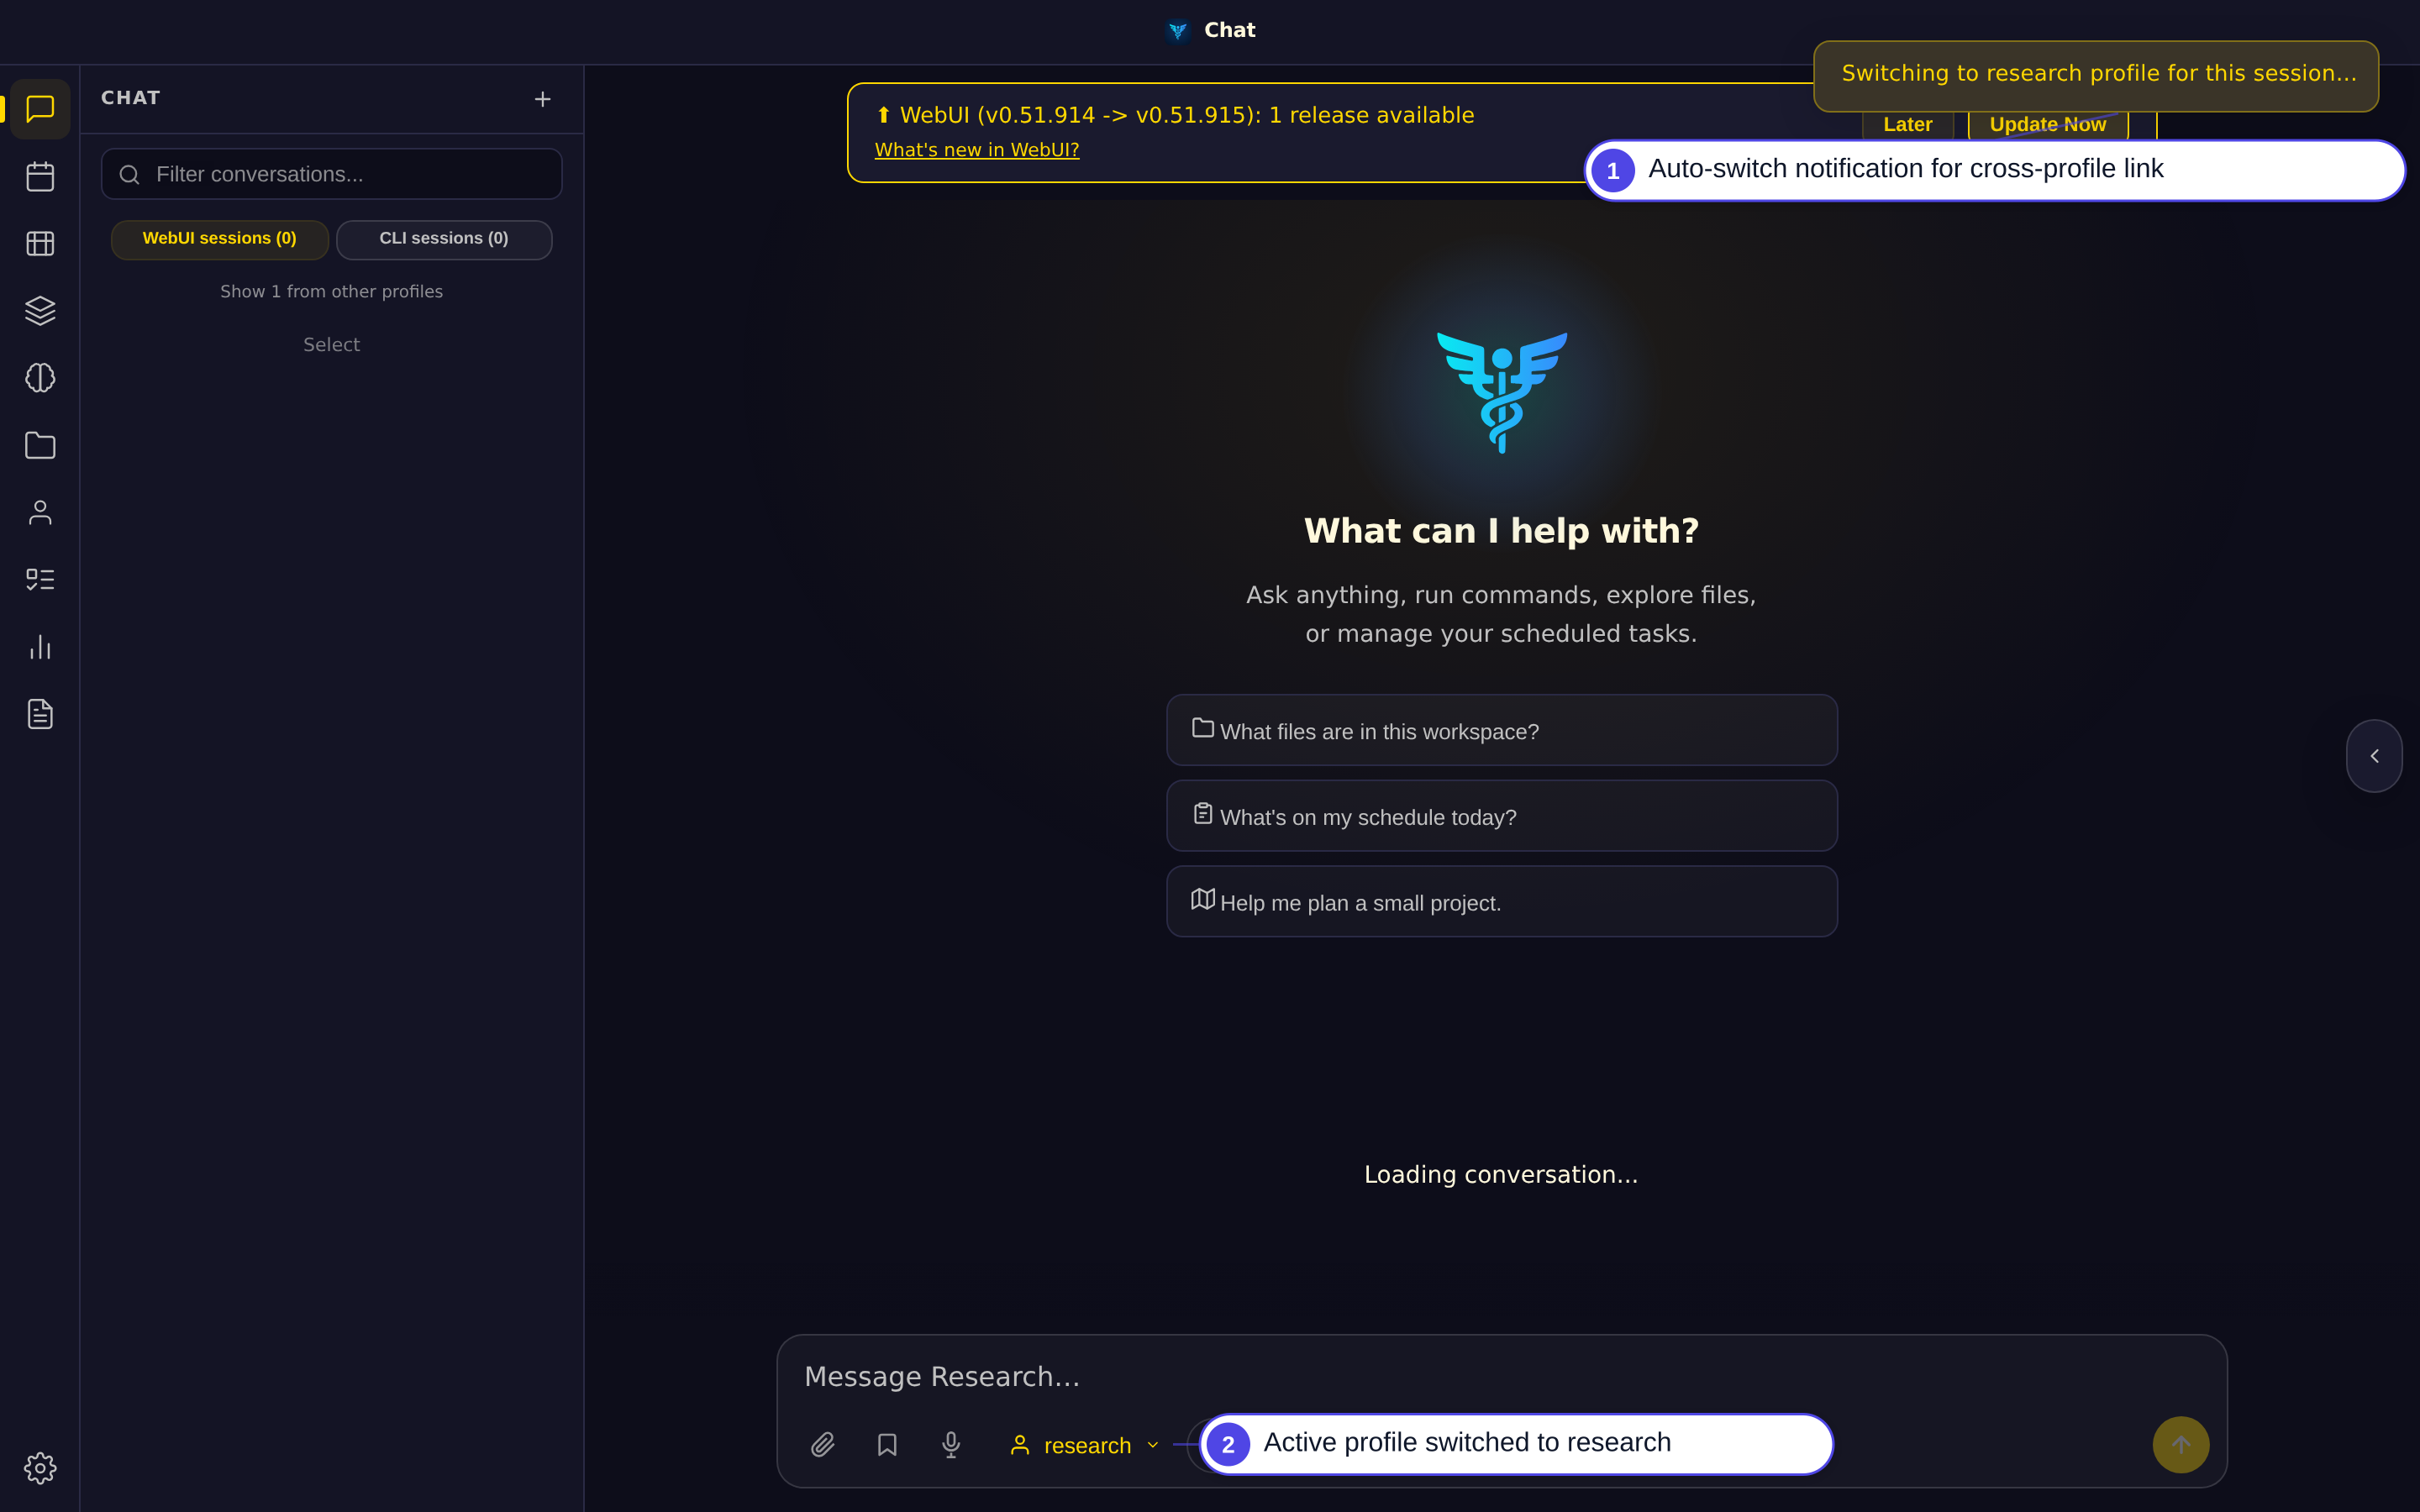
🎬 Cutter preview — PR #5728
|
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment
2 participants


Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Release: auto-switch profiles for cross-profile session links (#5419)
A valid
session://deep link to a session owned by a different Hermes profile used to look identical to a deleted session (404 → the frontend self-healed away, "Session not available in web UI"). Now GET/api/sessionreturns a structured 409session_profile_mismatchenvelope (error/code/session_id/profile ONLY — no transcript) when the owning profile is known, andloadSession()switches to the owning profile and retries once. Truly missing/deleted (or legacy None-profile) sessions keep the 404 self-heal.Source PR: #5419 by @harcek. Diff: +226 (api/routes.py, static/sessions.js, tests).
Maintainer changes + gate fixes (Codex + Fable)
_switchProfileForSessionLoadso a navigation during the profile switch (POST + list re-render) can't hijack the UI back to the old session._session_profileis truthy._profiles_matchcoercesNone→'default', so a truly-missing/legacy None-profile session under a non-default active profile would otherwise emit a uselessprofile:null409 — the frontend requires a truthy profile, so it fell into the generic error branch, skipped the 404 self-heal, and re-armed the SSE stream against a dead session id. Fixed on both detail branches + 2 mutation-checked regression tests._switchProfileForSessionLoadnow clears the sidebar skeleton + re-renders from cache on switch-POST failure (mirrors the Profile switch: polished loading skeletons (sidebar + workspace) — #4662 phase 1 #4671 canonical-switch catch), then rethrows — a failed switch no longer strands the sidebar on the skeleton.test_issue1611profile-isolation tests to the 409 contract while preserving the no-leak boundary assertion (envelope-key allowlist + explicit forbidden-key checks).Gate (all green)
/api/profiles); Finding-1 fix narrows it further..venv-missing-deps artifact — passes with deps, fix: auto-switch profiles for session links #5419 touches no TLS code).Attribution preserved: authored as @harcek + maintainer Co-authored-by. CHANGELOG credit.